
Direct teams
Run an authorised test when you need evidence on an exposed application or API. Review the target and accepted findings in one report, with references to supporting evidence and any negative controls.

Home / Features / Automated Penetration Testing
Automated penetration testing
Give GovernSafe an authorised base URL and a clear scope. The engine maps the exposed surface, runs bounded black-box tests, preserves the evidence, and reports findings that pass validation.
Beta access is available for controlled, authorised pilots.
Download the sample penetration test report →Who it is for
Run an authorised test when you need evidence on an exposed application or API. Review the target and accepted findings in one report, with references to supporting evidence and any negative controls.
Evaluate a repeatable testing workflow for approved client scopes, with evidence that can move into remediation and reporting.
How it works
Start with a base URL, approved boundaries, and the access mode for the test.
Discover routes, browser flows, forms, APIs, assets, and authentication surfaces that are inside scope.
Execute black-box checks across the mapped surface while keeping target state and the request trail available across the assessment.
Publish a finding only when request, response, browser, scanner, or matcher evidence passes the applicable validation rule.
Review each accepted finding with its severity, endpoint, validator, sources, supporting evidence references, and any negative controls.
Benchmark proof
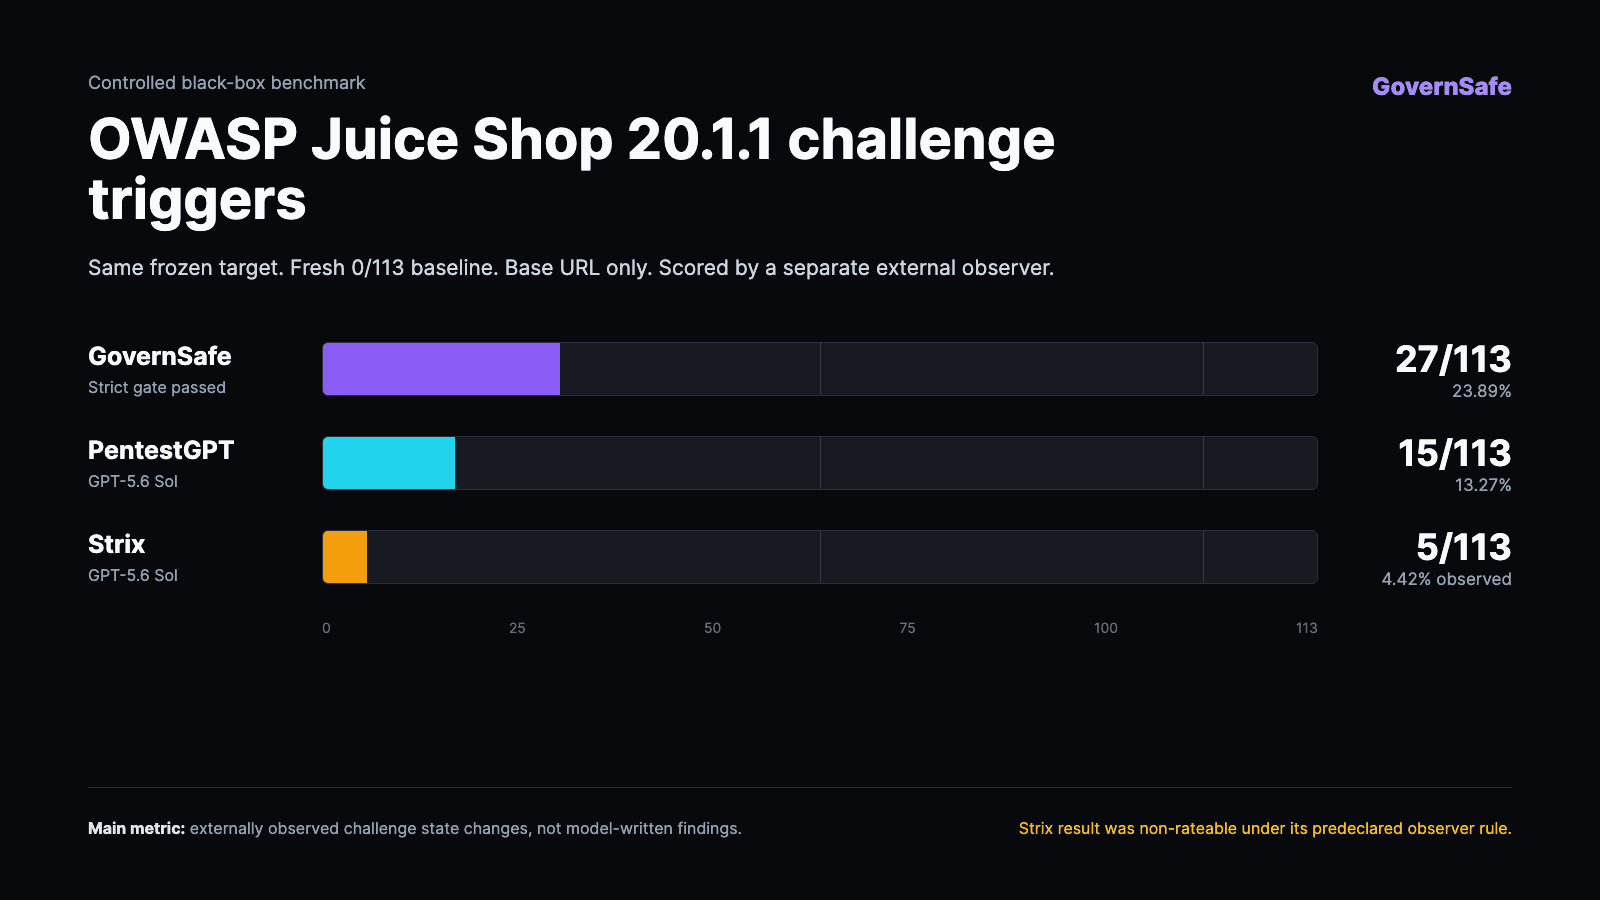
In a controlled OWASP Juice Shop 20.1.1 test, GovernSafe triggered 27 of 113 challenges. PentestGPT triggered 15. Strix triggered 5 observed, but its result was non-rateable under the predeclared observer rule. All three started from a clean target with a base URL and a generic authorised black-box instruction.
Read the benchmark and methodologyThe head-to-head figures use the same frozen target and external challenge observer. Other published systems used different targets, access modes, versions, or counting rules and are not presented here as a shared leaderboard.
GovernSafe does not replace a human-led penetration testing consultancy or guarantee that every vulnerability will be found. Coverage depends on the authorised scope, target state, access mode, and test configuration.
Inside a GovernSafe report
Download our full penetration test report for OWASP Juice Shop. See how validated findings become a clear record of risk, supporting evidence and remediation guidance.
Agentic sample pentesting report
85 pages · PDF
16 July 2026
35 validated finding records from an isolated lab test.
This sample covers an intentionally vulnerable lab application. It is a separate test from the published benchmark and does not predict results for another target.
In a controlled pilot, we will show you how GovernSafe maps the surface, validates evidence, and reports the result.